Question regarding DRMs
Hey guys, IceSeasons here.
After reading through all of the discussions in ScriptFodder regarding DRMs and such, I expressed some interest in creating a DRM of my own just for the sake of educational purposes and perhaps as a means of testing grounds. I have been developing some scripts for my own personal use and would like to inquire the ScriptFodder community the following:
- How does one create and develop a DRM, and does it require any networking or webhost in order to do it?
- How do you ensure that the DRM that is developed will be non-intrusive and user-friendly to the players, while ensuring the content of the script is not compromised?
- Is there any resources or tutorials available that can help to understand the creation and development of DRMs, along with its concepts and such?
I am not looking for a foolproof DRM or such, but I would rather like to learn how to create a basic one and such. I would greatly appreciate it if there are positive feedbacks regarding this, since I do hope that the community can at least help those who are new to coding and would like to inquire more about its operations and concepts of it.
I understand that this is rather a difficult time to be asking these kinds of questions, especially with the recent drama regarding ScriptEnforcer and DRMs. While people may form their own opinions about it, I do not wish this thread to be associated with it at any costs. This thread was built specifically on a desire to at least self-improve and for educational purposes, not as a mean to hurl opinions towards each other. If it does derail to that point, I will not hesitate to request for the thread to be locked down. There is no need for an argument thread here, and I certainly won’t welcome opinions here.
Keep the thread civil guys, I cannot stress this enough, and thanks a lot for helping me out! :D
Effective DRMs require webhosting yes, to keep track of what's going on with the script and to possibly revoke access from someone who looks like they might be leaking it by having it on shit tons of different communities.
To ensure customer satisfcation you want your DRM to be as invisible as possible, so people don't have to worry about it, if you don't make any thing like Linking servers or something that takes a lot of "brain power" then you should be good, a simple steamid or paypal transaction id activation is good enough.
Not really, it's all in common sense you just need basic programming knowledge to know how to make one tbh.
ByLunaversity.xyz 💮at 29th of January 2017 09:28:27
Effective DRMs require webhosting yes, to keep track of what's going on with the script and to possibly revoke access from someone who looks like they might be leaking it by having it on shit tons of different communities.To ensure customer satisfcation you want your DRM to be as invisible as possible, so people don't have to worry about it, if you don't make any thing like Linking servers or something that takes a lot of "brain power" then you should be good, a simple steamid or paypal transaction id activation is good enough.Not really, it's all in common sense you just need basic programming knowledge to know how to make one tbh.
Haha, I see. Thanks a lot for your input though! Is having trackers about the same as using DRMs? And can reading someone's code about DRM help to give a sense of idea as to how to establish one?
ByIceSeasonsat 29th of January 2017 09:46:14
Haha, I see. Thanks a lot for your input though! Is having trackers about the same as using DRMs? And can reading someone's code about DRM help to give a sense of idea as to how to establish one?
Eh, reading someone elses DRM code wont help because the main idea of it is to be as Secure as possible. So how everyone goes about making a DRM is different than someone elses. The most I could tell you is that you will need a webserver. ScriptFodder also helps the drm scene in some way with there File String Replacements Ontop of this they also have an API which can help too. But like Luna said. You could authenticate users via PayPal transaction ID.
Hello,
I use a DRM outside of scriptfodder to run sfportal. This is basically how it works.
User purchases on Scriptfodder. User logs into our website. System checks Scriptfodder account status, what they are banned for and from then handles accordingly. User Enters the domain in which they would like to run the files on. (could be adapted to gameserver ips aswell) Then our system generates a personal encoded version for each user. (Domain locked, user locked, trackable to a domain and more importantly the scriptfodder user) This way if you get a leaker you can see it very easily. However it is very recommendable to have some sort of license api. using a mix of static and dynamic codes.
For example:
Check "steamid", "transactionid" and "scriptid" with match on your api. (statics), Also call the server ip and port from the script dynamically and put this into a post request on successful data match + pair this with a time log of last check etc. You can also do things like if server/site hasn't done a callback in X period of time then die() or kill/impair a core function/s. Make sure it can't be triggered easily e.g. do a timed check or event check. In addition to this you can hide certain codes/details on the mysql which the server can send in response in a similar way to a REST api where the actual script is dependant on certain code to run. Without the callbacks it wont work. The way you can do this would vary based on the script and how well you can implement it.
Hope this helps.
Kind Regards
Bl4d3z
I think a simple thing to do (and yes this kind of goes out of topic a little because it's not exactly a drm) is to make a stat tracker. On this stat tracker you can just track people who use it and use file string replacements to get there steamid and if you see a steamid more then x times you now know that steamid leaked your script... now it won't do anything about it but you can confront the guy... I have made a stat tracker before but I have also seen this kind of thing here with mr. P
https://scriptfodder.com/community/threads/2116-alexis-probable-leak-of-awarn2-script
ByXxLMM13xXgaming™at 3rd of February 2017 11:20:31
I think a simple thing to do (and yes this kind of goes out of topic a little because it's not exactly a drm) is to make a stat tracker. On this stat tracker you can just track people who use it and use file string replacements to get there steamid and if you see a steamid more then x times you now know that steamid leaked your script... now it won't do anything about it but you can confront the guy... I have made a stat tracker before but I have also seen this kind of thing here with mr. Phttps://scriptfodder.com/community/threads/2116-alexis-probable-leak-of-awarn2-script
I like this stat-tracker idea. What I would do is create a panel on a web server using the ScriptFodder API and/or paypal transaction ids. When the user installs the script, it would send the ID to your web server. Your web server then would check if the installing user owns the script, and if not it would flag it as potentially a leak. This could be useful because it shows who installed your script, when they installed it, and how many scripts do they have installed under their steamid.
Best way of doing a DRM system would be to have multiple callbacks where the api would release segments of code however garrysmod wouldn't support this without a dll/so extension installed which in theory could be made however it would take too long to produce and the dll would need to be compiled for each and every developers addons uniquely so that certain callbacks give certain replies. You could do it in a scriptenforcer type way but again it would take too long to produce it and it would mean forever updating your servers.
Honestly just keeping it to tracking is fine enough. What server is using it, the owner of the addon, etc. Doesn't have any fallback if they remove it, but I think people are too worried about their stuff being leaked.
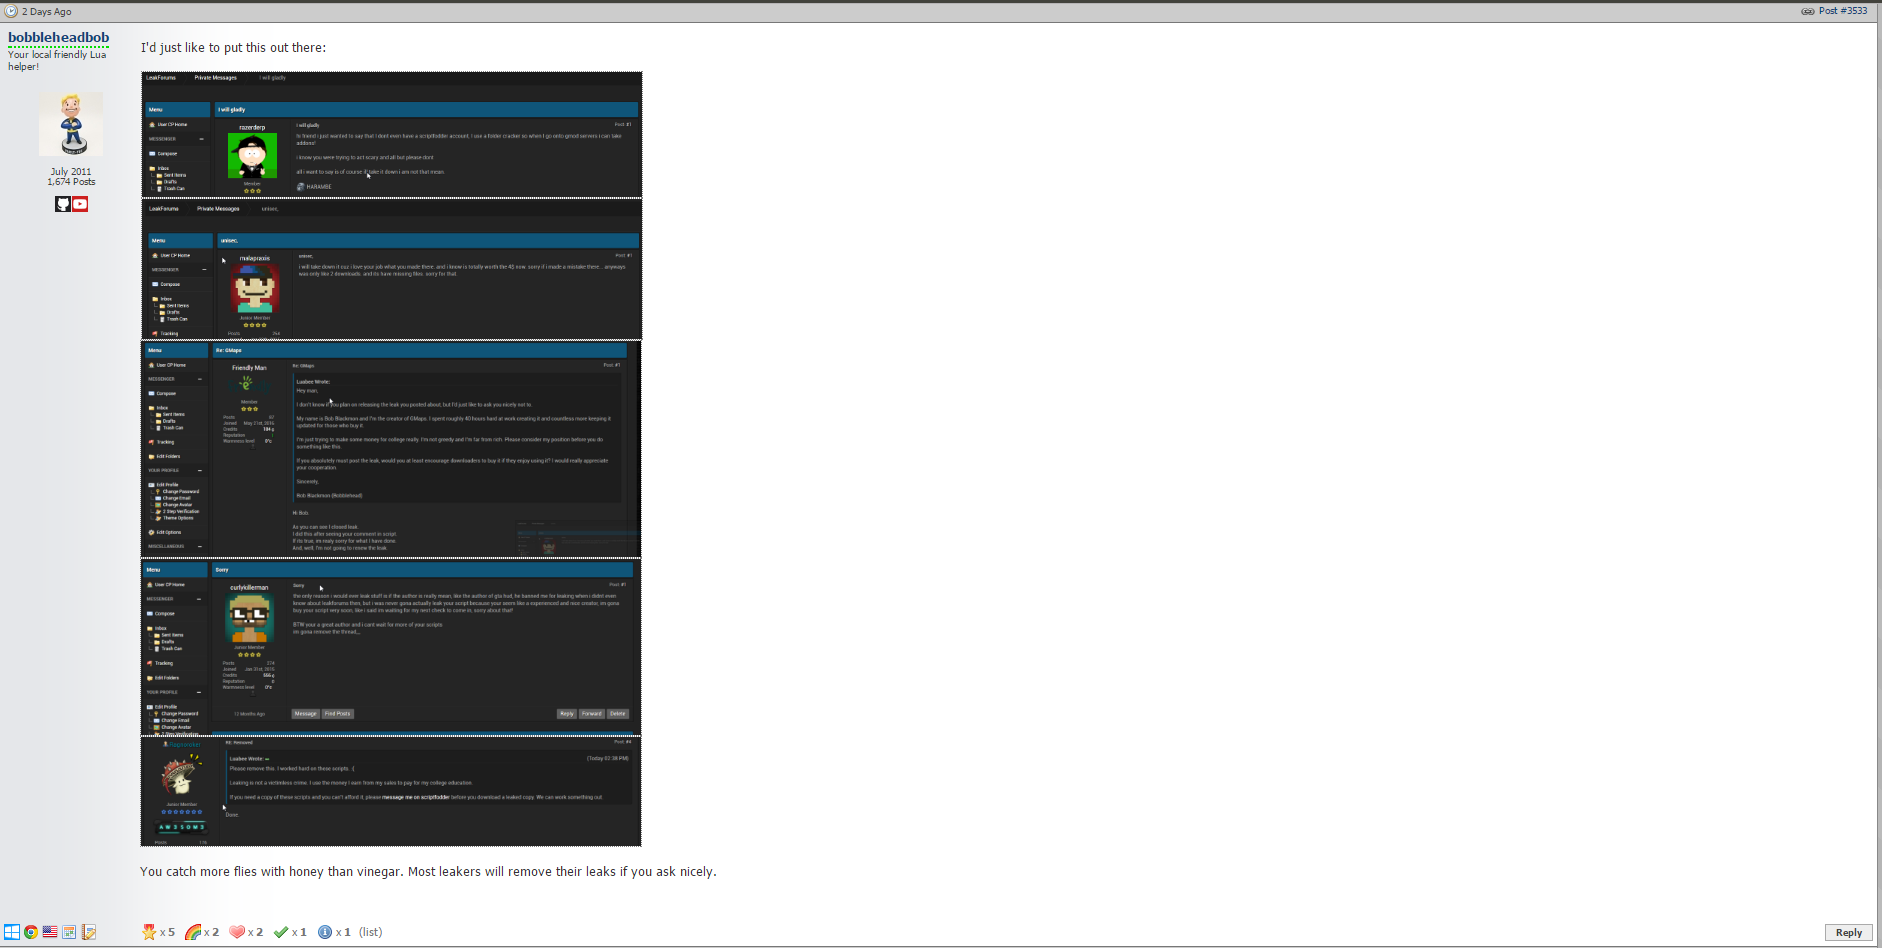
As Bobblehead as shown you can simply ask, and more likely than naught they'll agree.